SlowMist Finds Malicious Udesk Scripts Stealing Login Data and Swapping Crypto Addresses
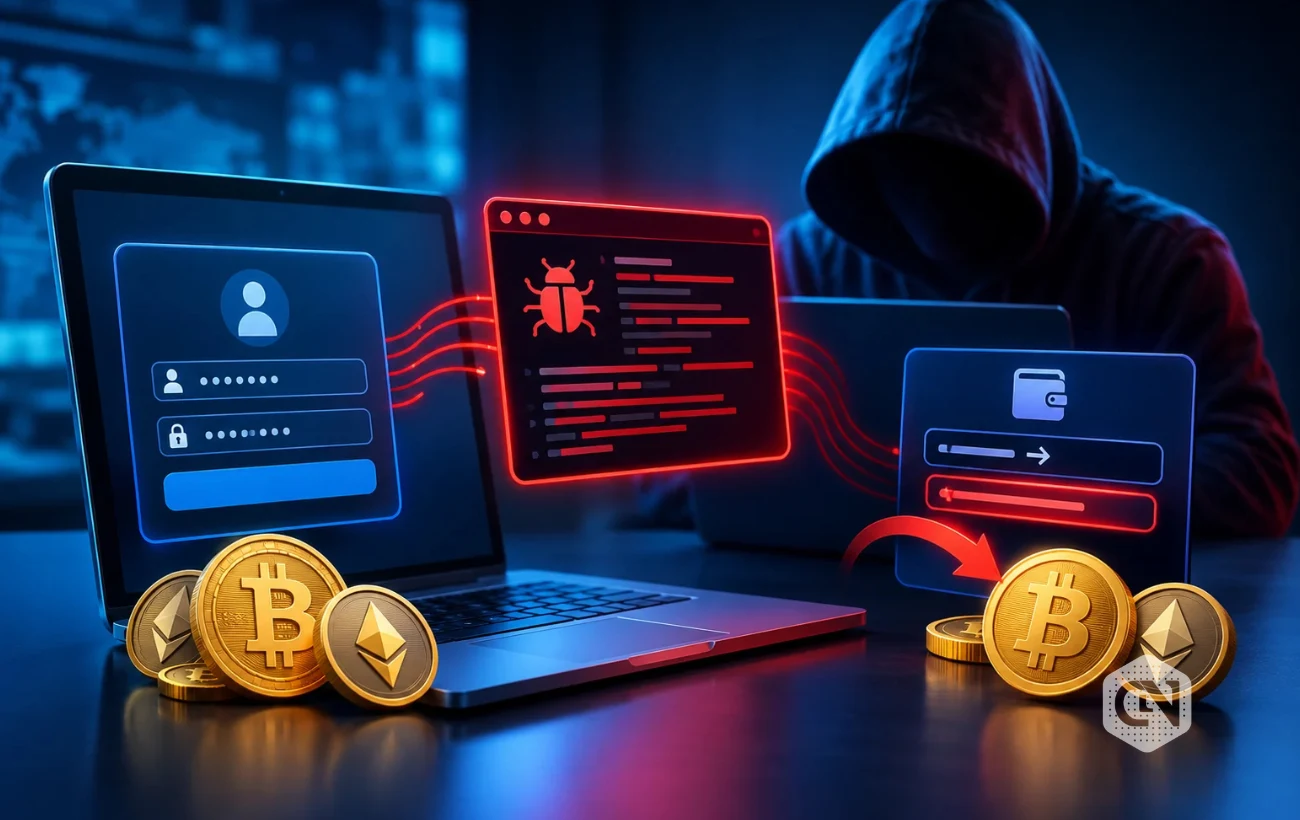
Blockchain security firm SlowMist has identified malicious Javascript injected into scripts associated with Udesk’s customer-service system, warning that the code can expose sensitive user information and interfere with cryptocurrency transfers. The firm exposed two JavaScript samples udeskApi.2026-10-16.cached.js and deeps.js, tracing how a remote script could collect browser data and modify deposit addresses. The findings point to two distinct risks: stolen login information could enable account or session impersonation, while address substitution could cause users to send funds to an unintended recipient. The report does not confirm that a specific platform was compromised or that any cryptocurrency was stolen.
You are reading an excerpt. CryptoNewsZ wrote and owns the full article.
Continue reading at cryptonewsz.com