Passport wallet maker links phishing emails to leaked Cloudflare keys
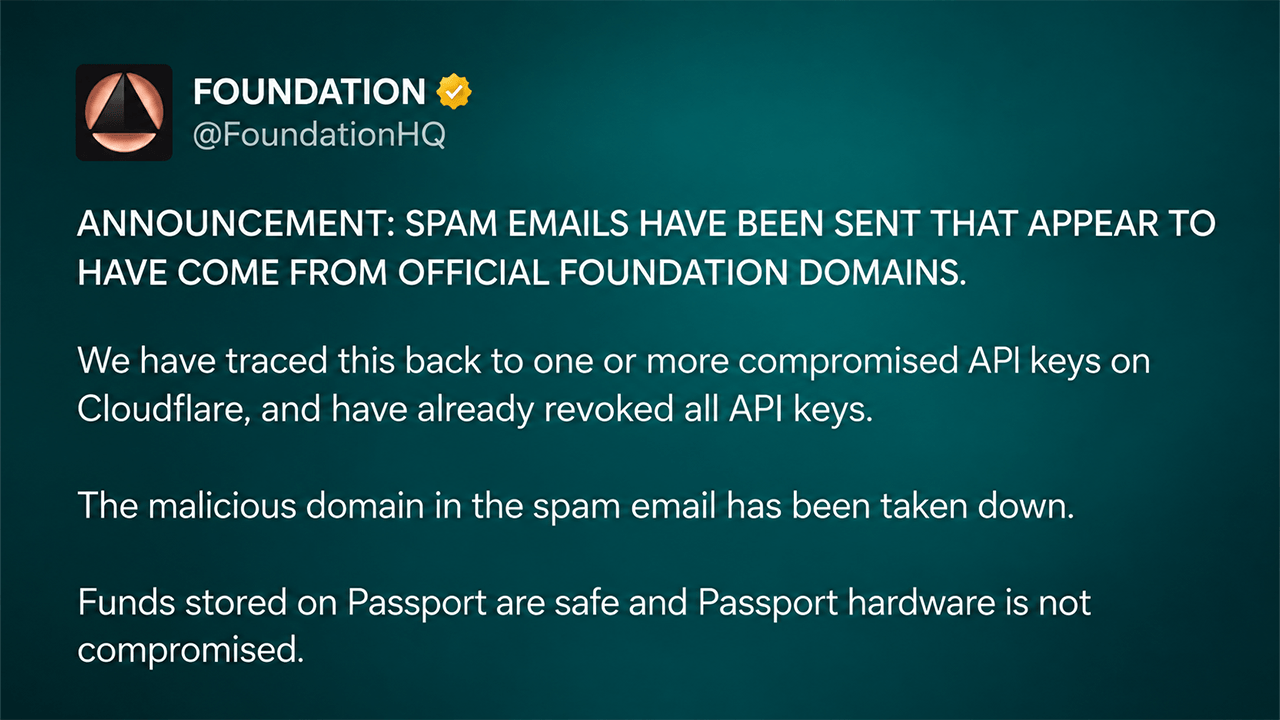
Community Trust Score Verified 82 % Real Verified 34 votes Updated 12 minutes ago Foundation, the maker of the Passport Bitcoin-only hardware wallet, stated that phishing emails sent to customers from the company’s own domains were the result of compromised Cloudflare API keys. The company announced on X on Monday, October 26, 2026, that it has revoked all affected keys and taken down the malicious domain used in the scam. The fraudulent messages arrived on Sunday under an urgent recall banner.
You are reading an excerpt. The Currency Analytics wrote and owns the full article.
Continue reading at thecurrencyanalytics.com